Agent Security
Decide API before side effects: allow, deny, or pending
What is Agent Security?
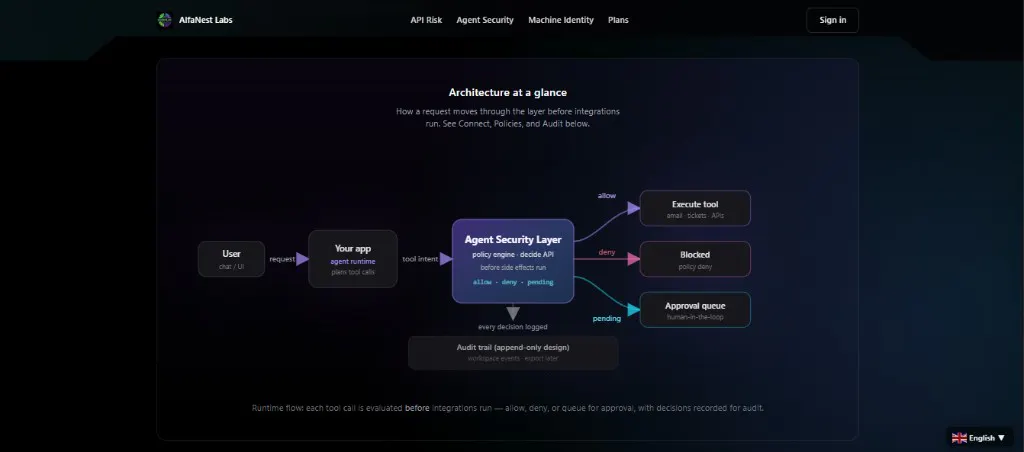
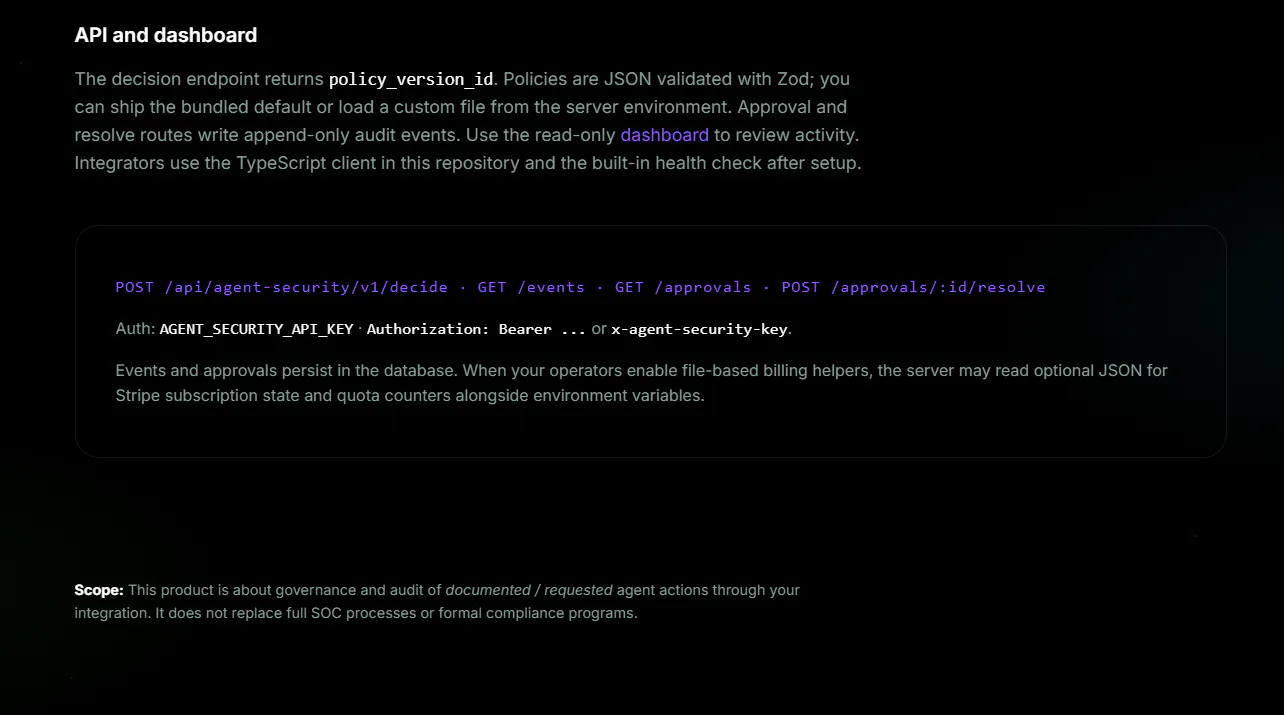
Agents plan tool calls. Agent Security sits between the runtime and integrations (email, tickets, APIs). Each call hits the policy engine (decide API) before side effects run: allow, deny, or pending. Allow executes the tool. Deny blocks it. Pending goes to a human-in-the-loop approval queue. Every decision is recorded on an append-only audit trail (workspace events, export later).
Screenshots
?
No comments yet. Be the first!