Echidra
Deceptive honeypot + attacker classifier, fully self-hosted
What is Echidra?
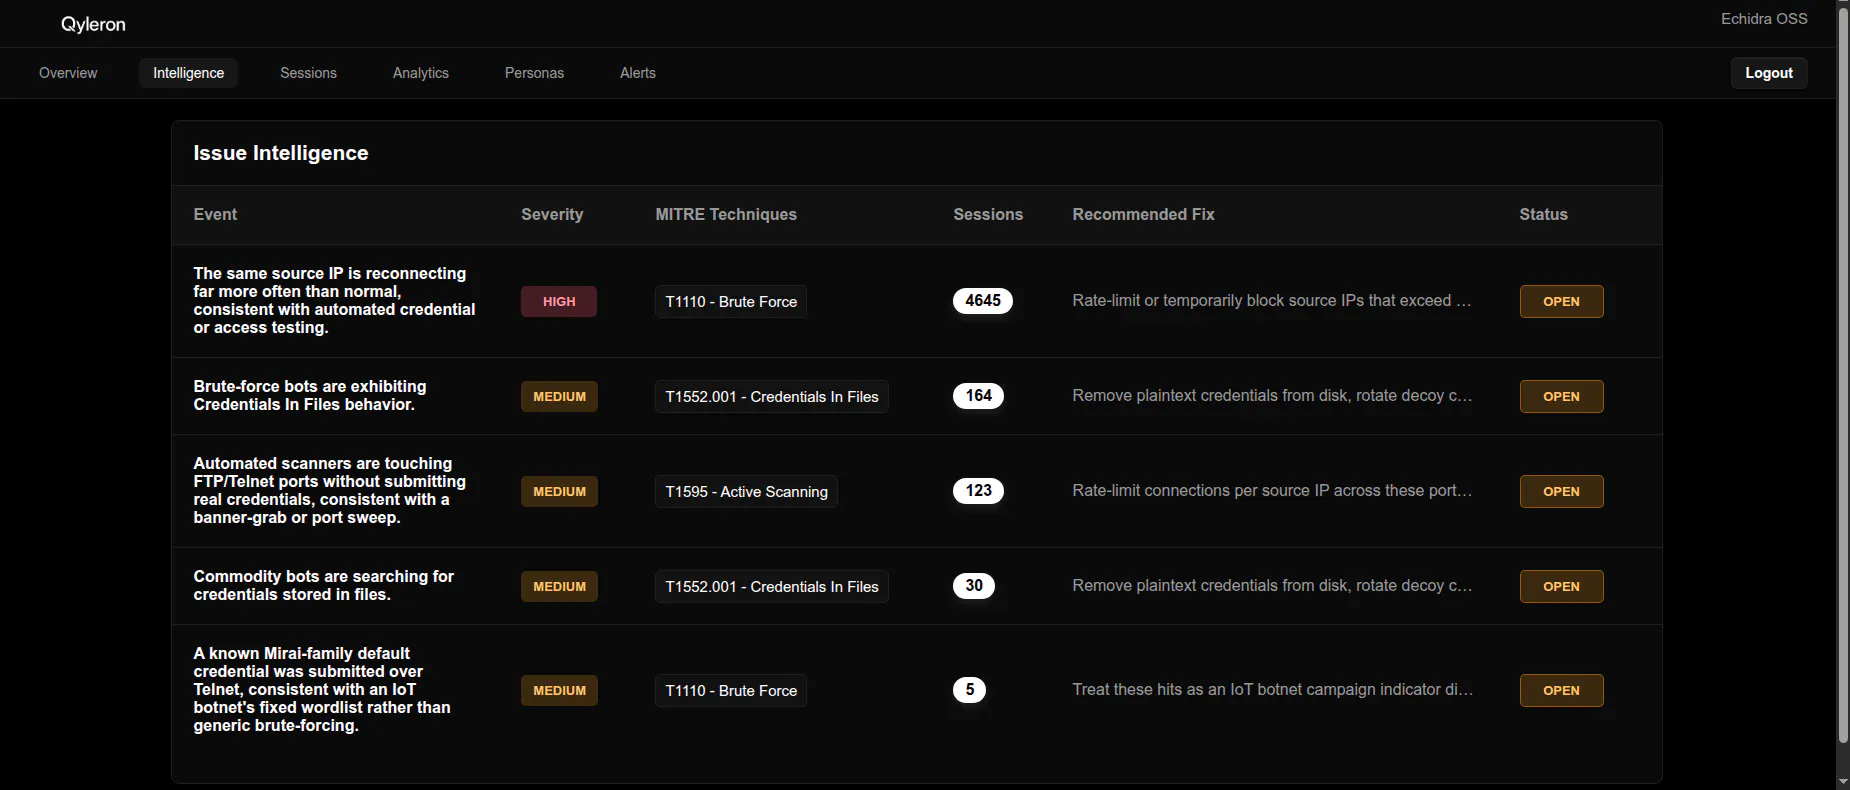
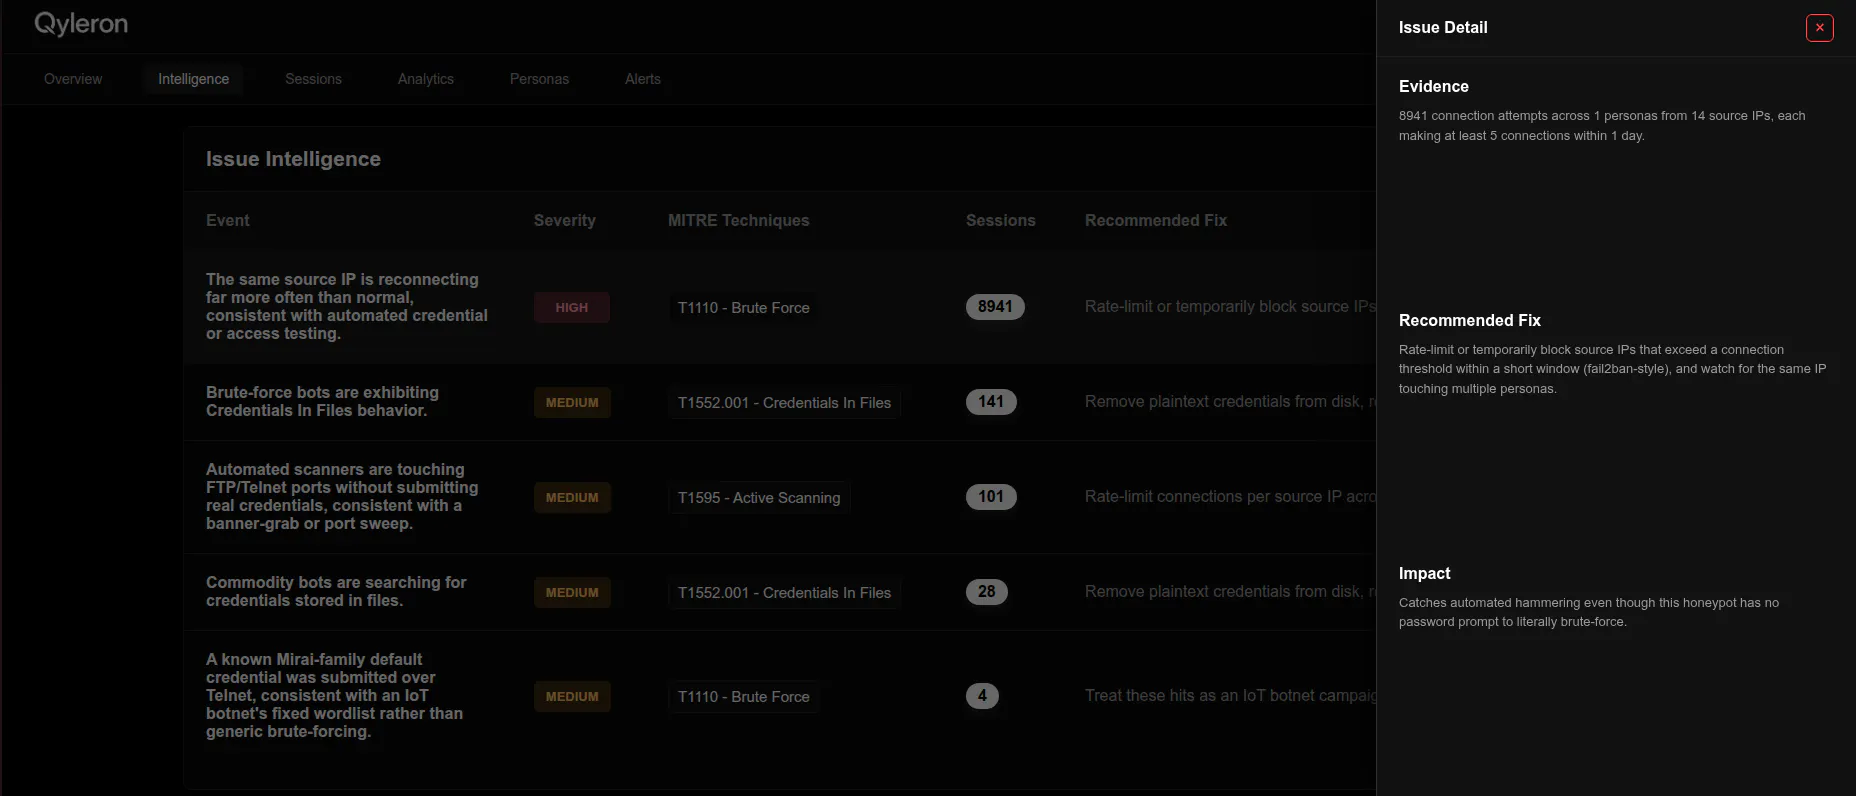
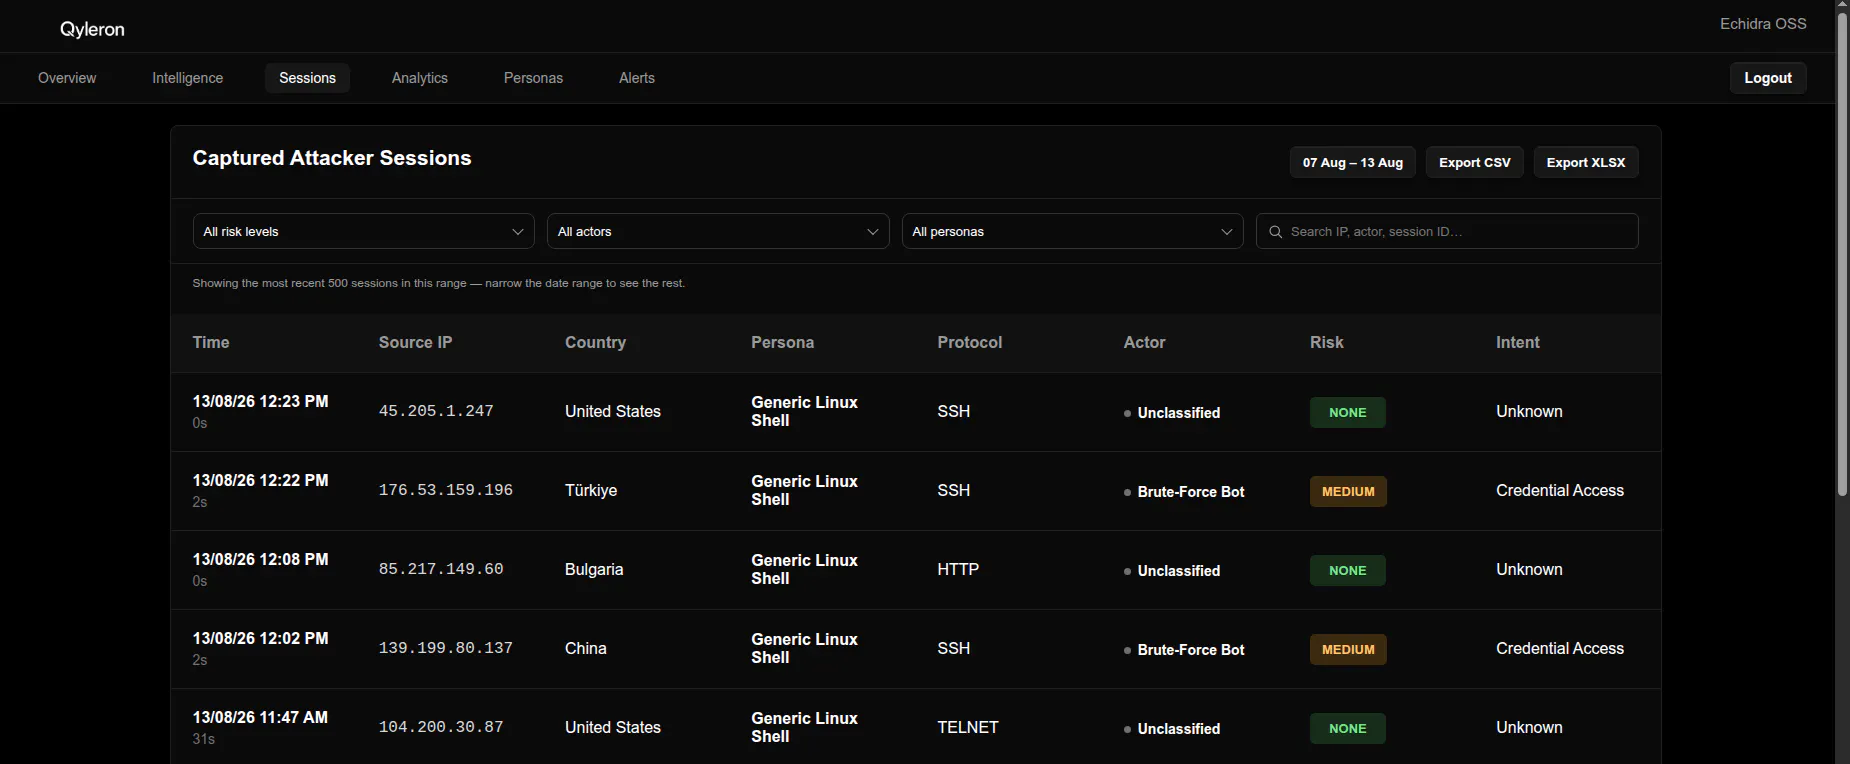
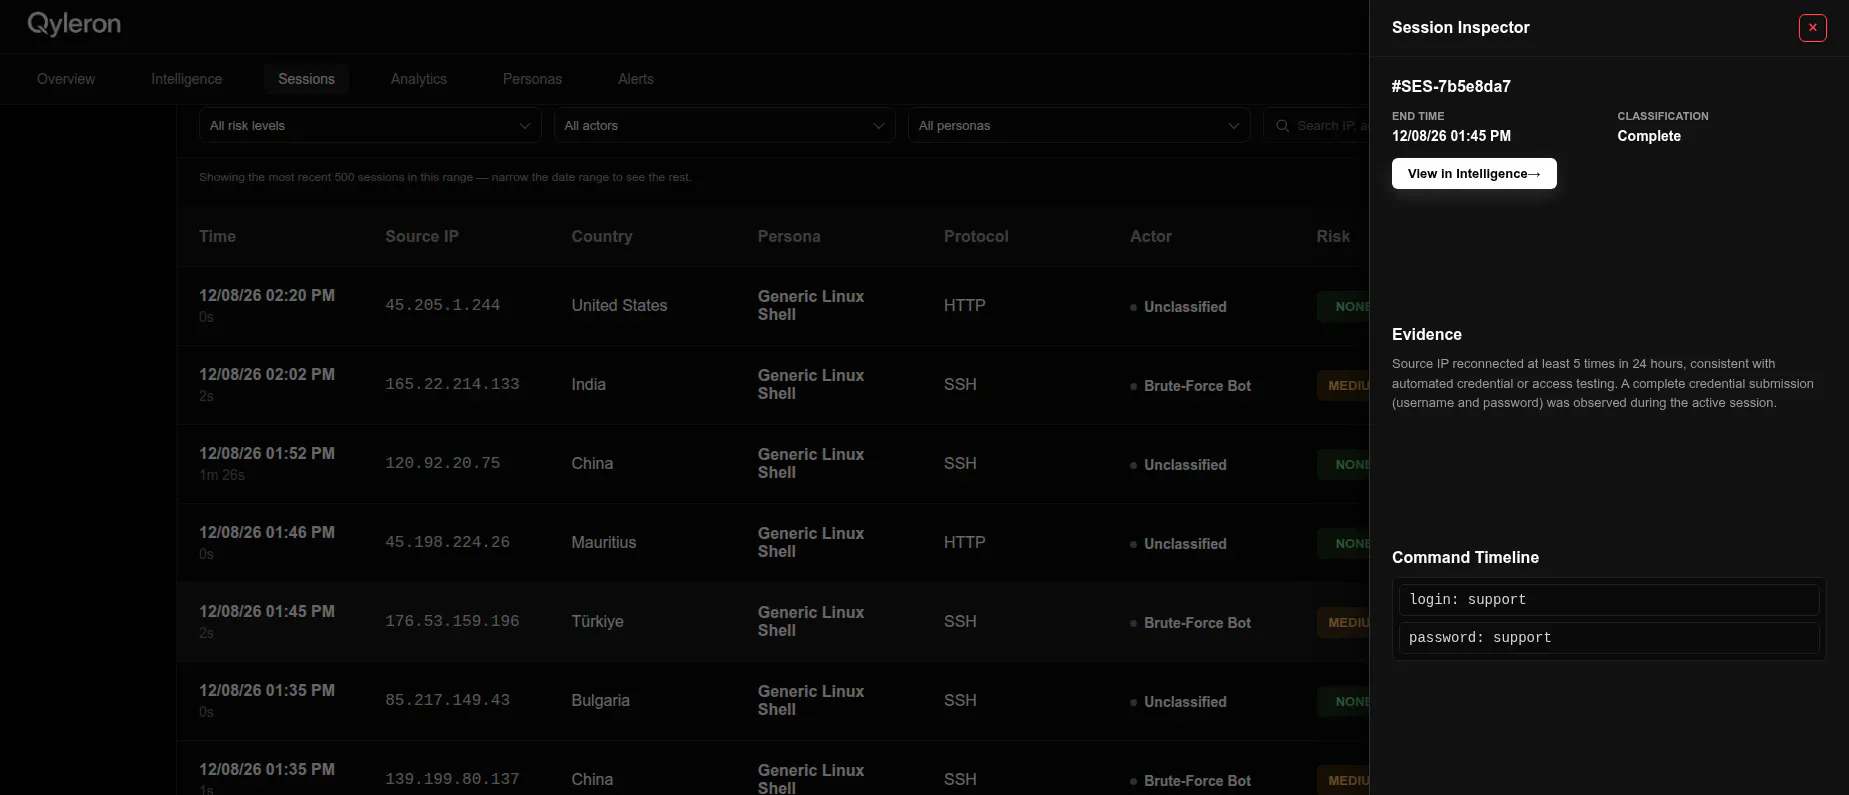
Most honeypots stop at logging connections. Echidra classifies them deterministic YAML rules turn each session into an actor label, risk score, MITRE ATT&CK tags, and a recommended fix, no opaque ML model deciding your risk score. It's also multi-protocol out of the box (SSH-shell, HTTP, FTP, Telnet) with a full self-hosted dashboard, not just a single-service logger. Fully open source, AGPLv3, nothing phones home — you own the data and can audit exactly why a session got its label.
Screenshots
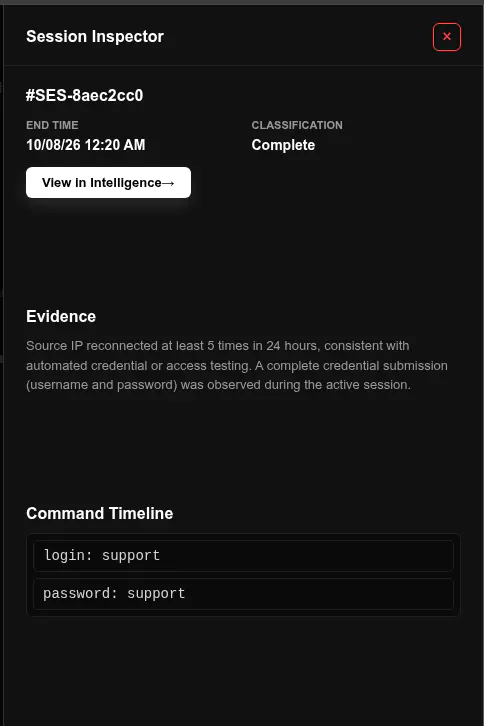
?
No comments yet. Be the first!